Closing the AI Governance Gap
Notes from a conversation with senior executives on enterprise AI adoption and control
There is a quiet gap. Personal AI tools are showing up on corporate expense reports. Corporate AI tools are being used for personal side projects. The AI adoption is real - the governance isn't. 💡
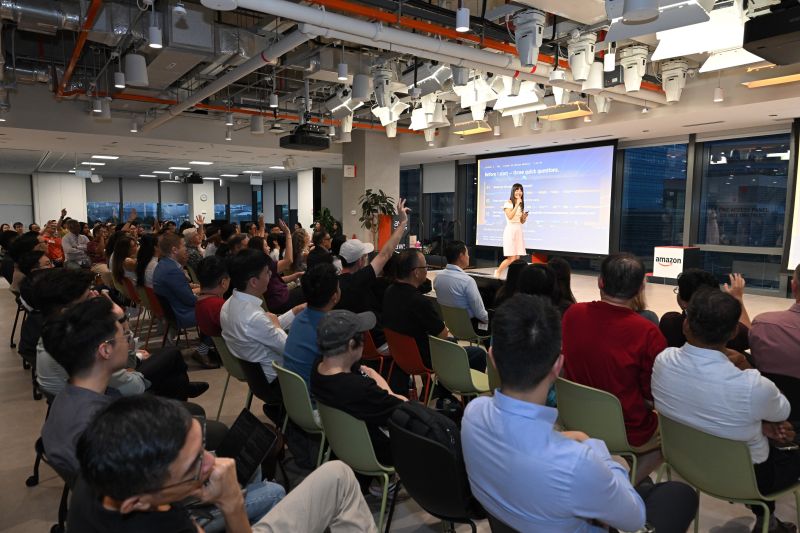
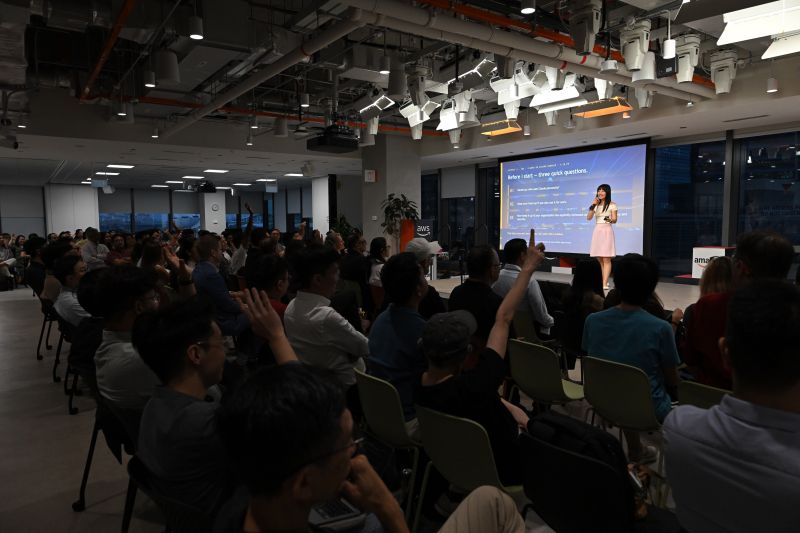
Last week I spoke to hundreds of the most senior executives in Singapore - in collaboration with the Claude Singapore Community and Anthropic - about the question I hear in every enterprise AI conversation across APAC:
How do you close the gap between how AI is actually used and how it's governed?
The answer isn't 'ban the tools.' It's to offer something with security, privacy, compliance, and governance built in from day one.
'Stored here' and 'processed here' are different promises
Your data at rest is like money in a vault - it sits where you put it. An inference request is a card swipe - and the swipe may clear through a different geography.
You need to understand the storage, processing, access, and downstream flows. Then you have a residency answer. Otherwise, you only have a residency assumption.
This distinction matters deeply for regulated industries and for organisations navigating data sovereignty requirements across ASEAN. The promise of 'your data stays in Singapore' needs to be unpacked: which data, at which stage, under which operation? 🎯
You don't have to pick one operating model only
You need to know which one fits which use case.
There are multiple operating models - each has different governance boundaries, different data processing relationships, and different commercial structures. Many organisations run more than one simultaneously.
For example: governed seats for productivity, controlled infrastructure for regulated workloads, and developer-first surfaces for speed.
The organisations I see moving fastest aren't trying to force every use case into a single procurement box. They're building a portfolio of deployment patterns, each with clear guardrails.
Governance is not a checklist
The organisations pulling ahead are designing systems where non-compliance is structurally impossible.
Enforceable policy over paper policy. Denied-by-default over approved-by-memo.
The question isn't whether you have a compliance statement - it's whether your infrastructure can actually enforce it. 🔹
This is where the human-first AI lens becomes operational. Governance frameworks that empower teams to move quickly and safely are the ones that treat compliance as architecture, not paperwork. They amplify human judgment by removing ambiguity at the system level.
The energy in the room
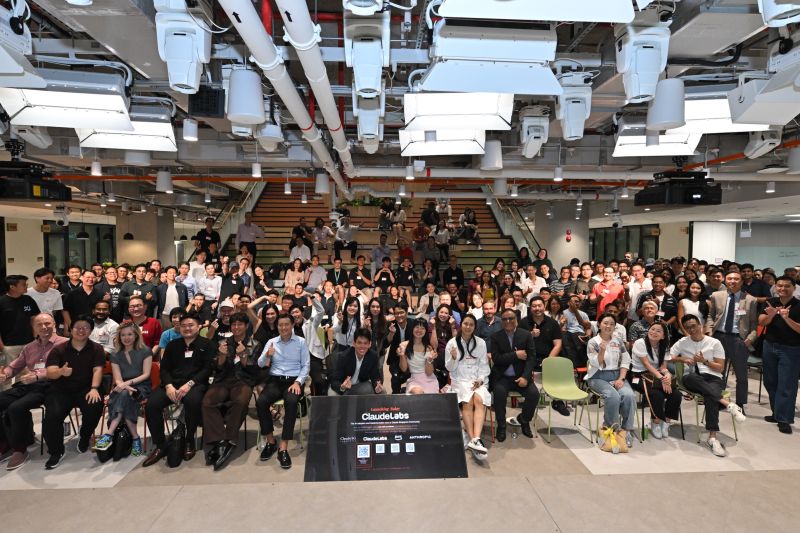
This session was a collaboration with the Claude Singapore Community's Freddy Lim, the Anthropic team including Daragh McGough and Eric C, as well as my AWS colleagues Mark Tay, Jake Khoo, and Karen Teo. I'm grateful for the incredible energy in the room. 🙏
The questions from the audience were sharper than most board decks I've read. CIOs, CISOs, and CTOs wrestling with the same tension: how do we enable innovation without losing control?
If your organisation is navigating the tension between AI adoption and governance - including data sovereignty - I'd love to hear how you're solving it. Drop a comment or reach out directly.
Together, we can close the gap between adoption and governance. More soon. ✨
#AlwaysDay1 #EnterpriseAI #AIGovernance #DataSovereignty #ResponsibleAI #AIStrategy #GenAI
Gallery
The views and opinions expressed in this post are my own and do not necessarily reflect those of my employer or any organisation I am affiliated with.